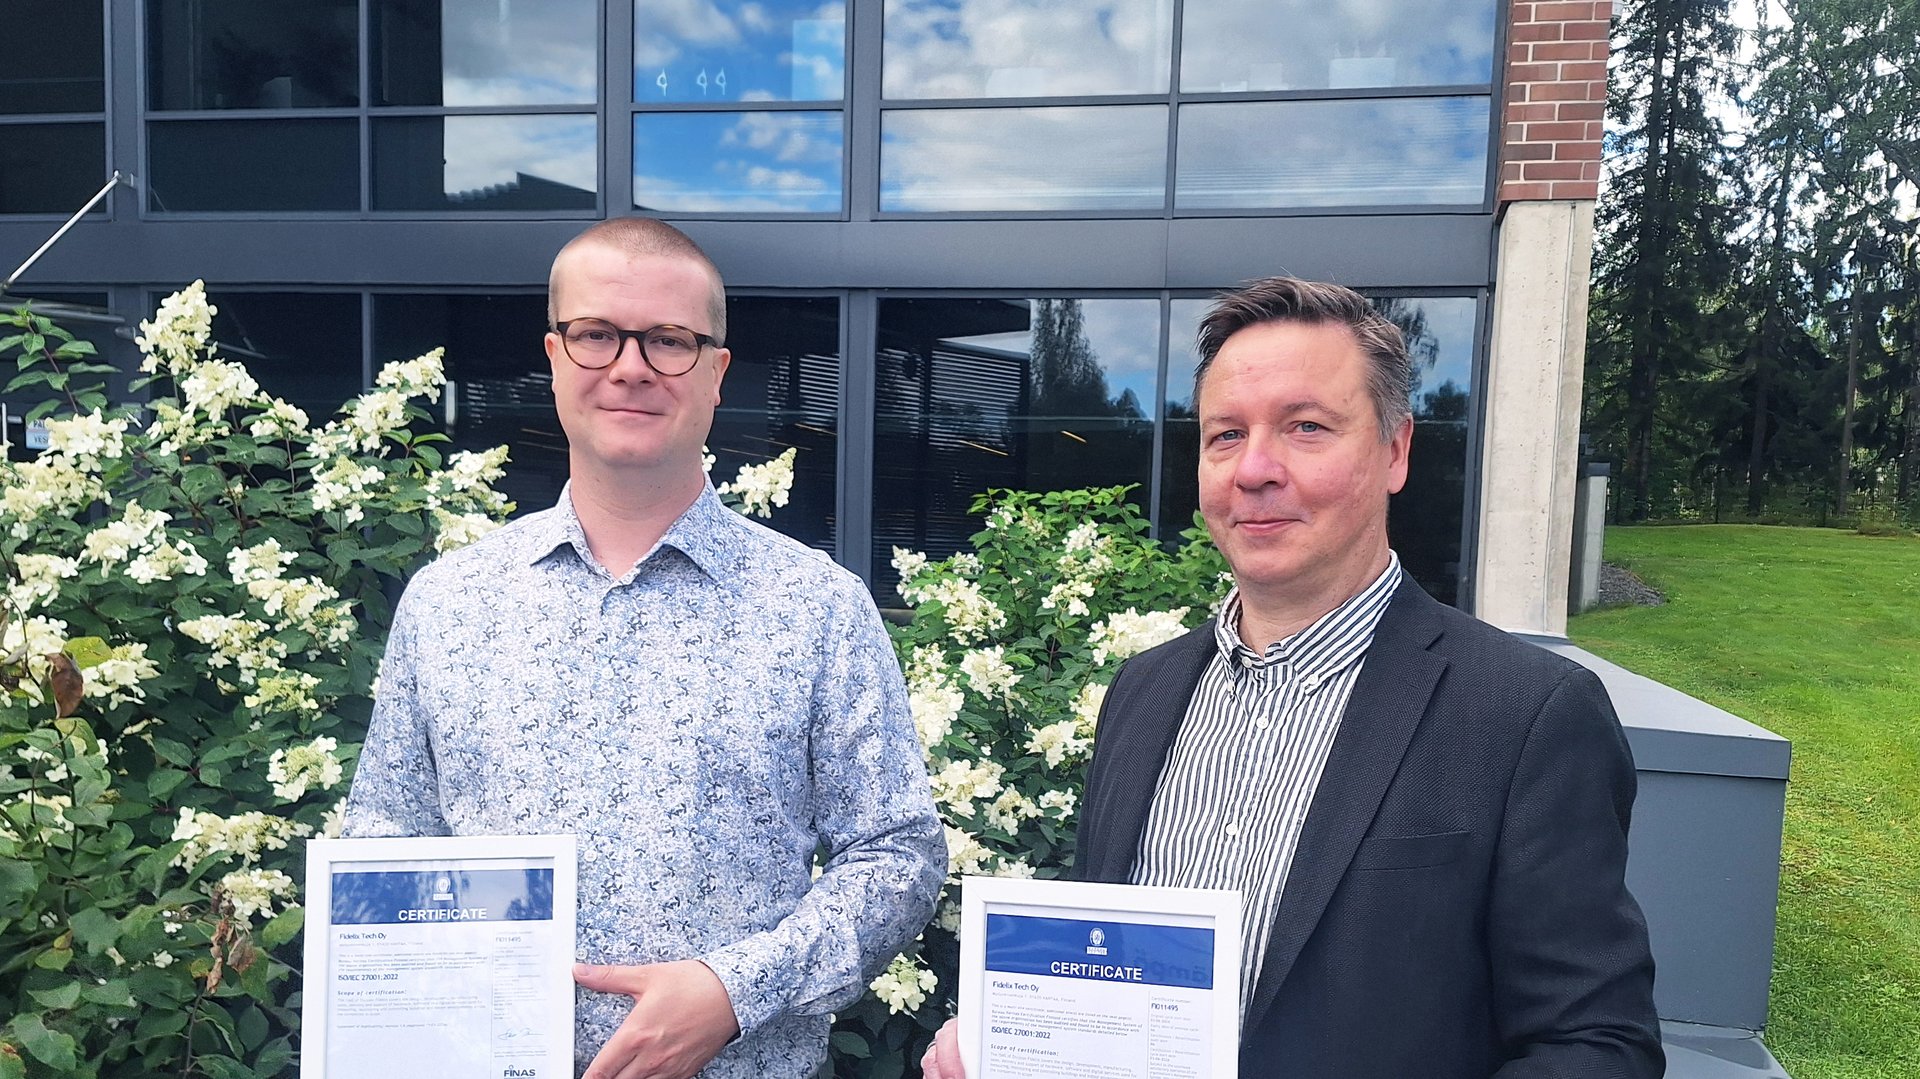
Fidelix companies Fidelix Tech Oy, EcoGuard AB, Lansen Systems AB and Larmia Control AB have been granted ISO/IEC 27001:2022 certification for information security by Bureau Veritas.
The certification covers the design, development, manufacturing, sales, delivery and support of hardware, software and digital services for buildings and indoor environments across the certified Fidelix companies.
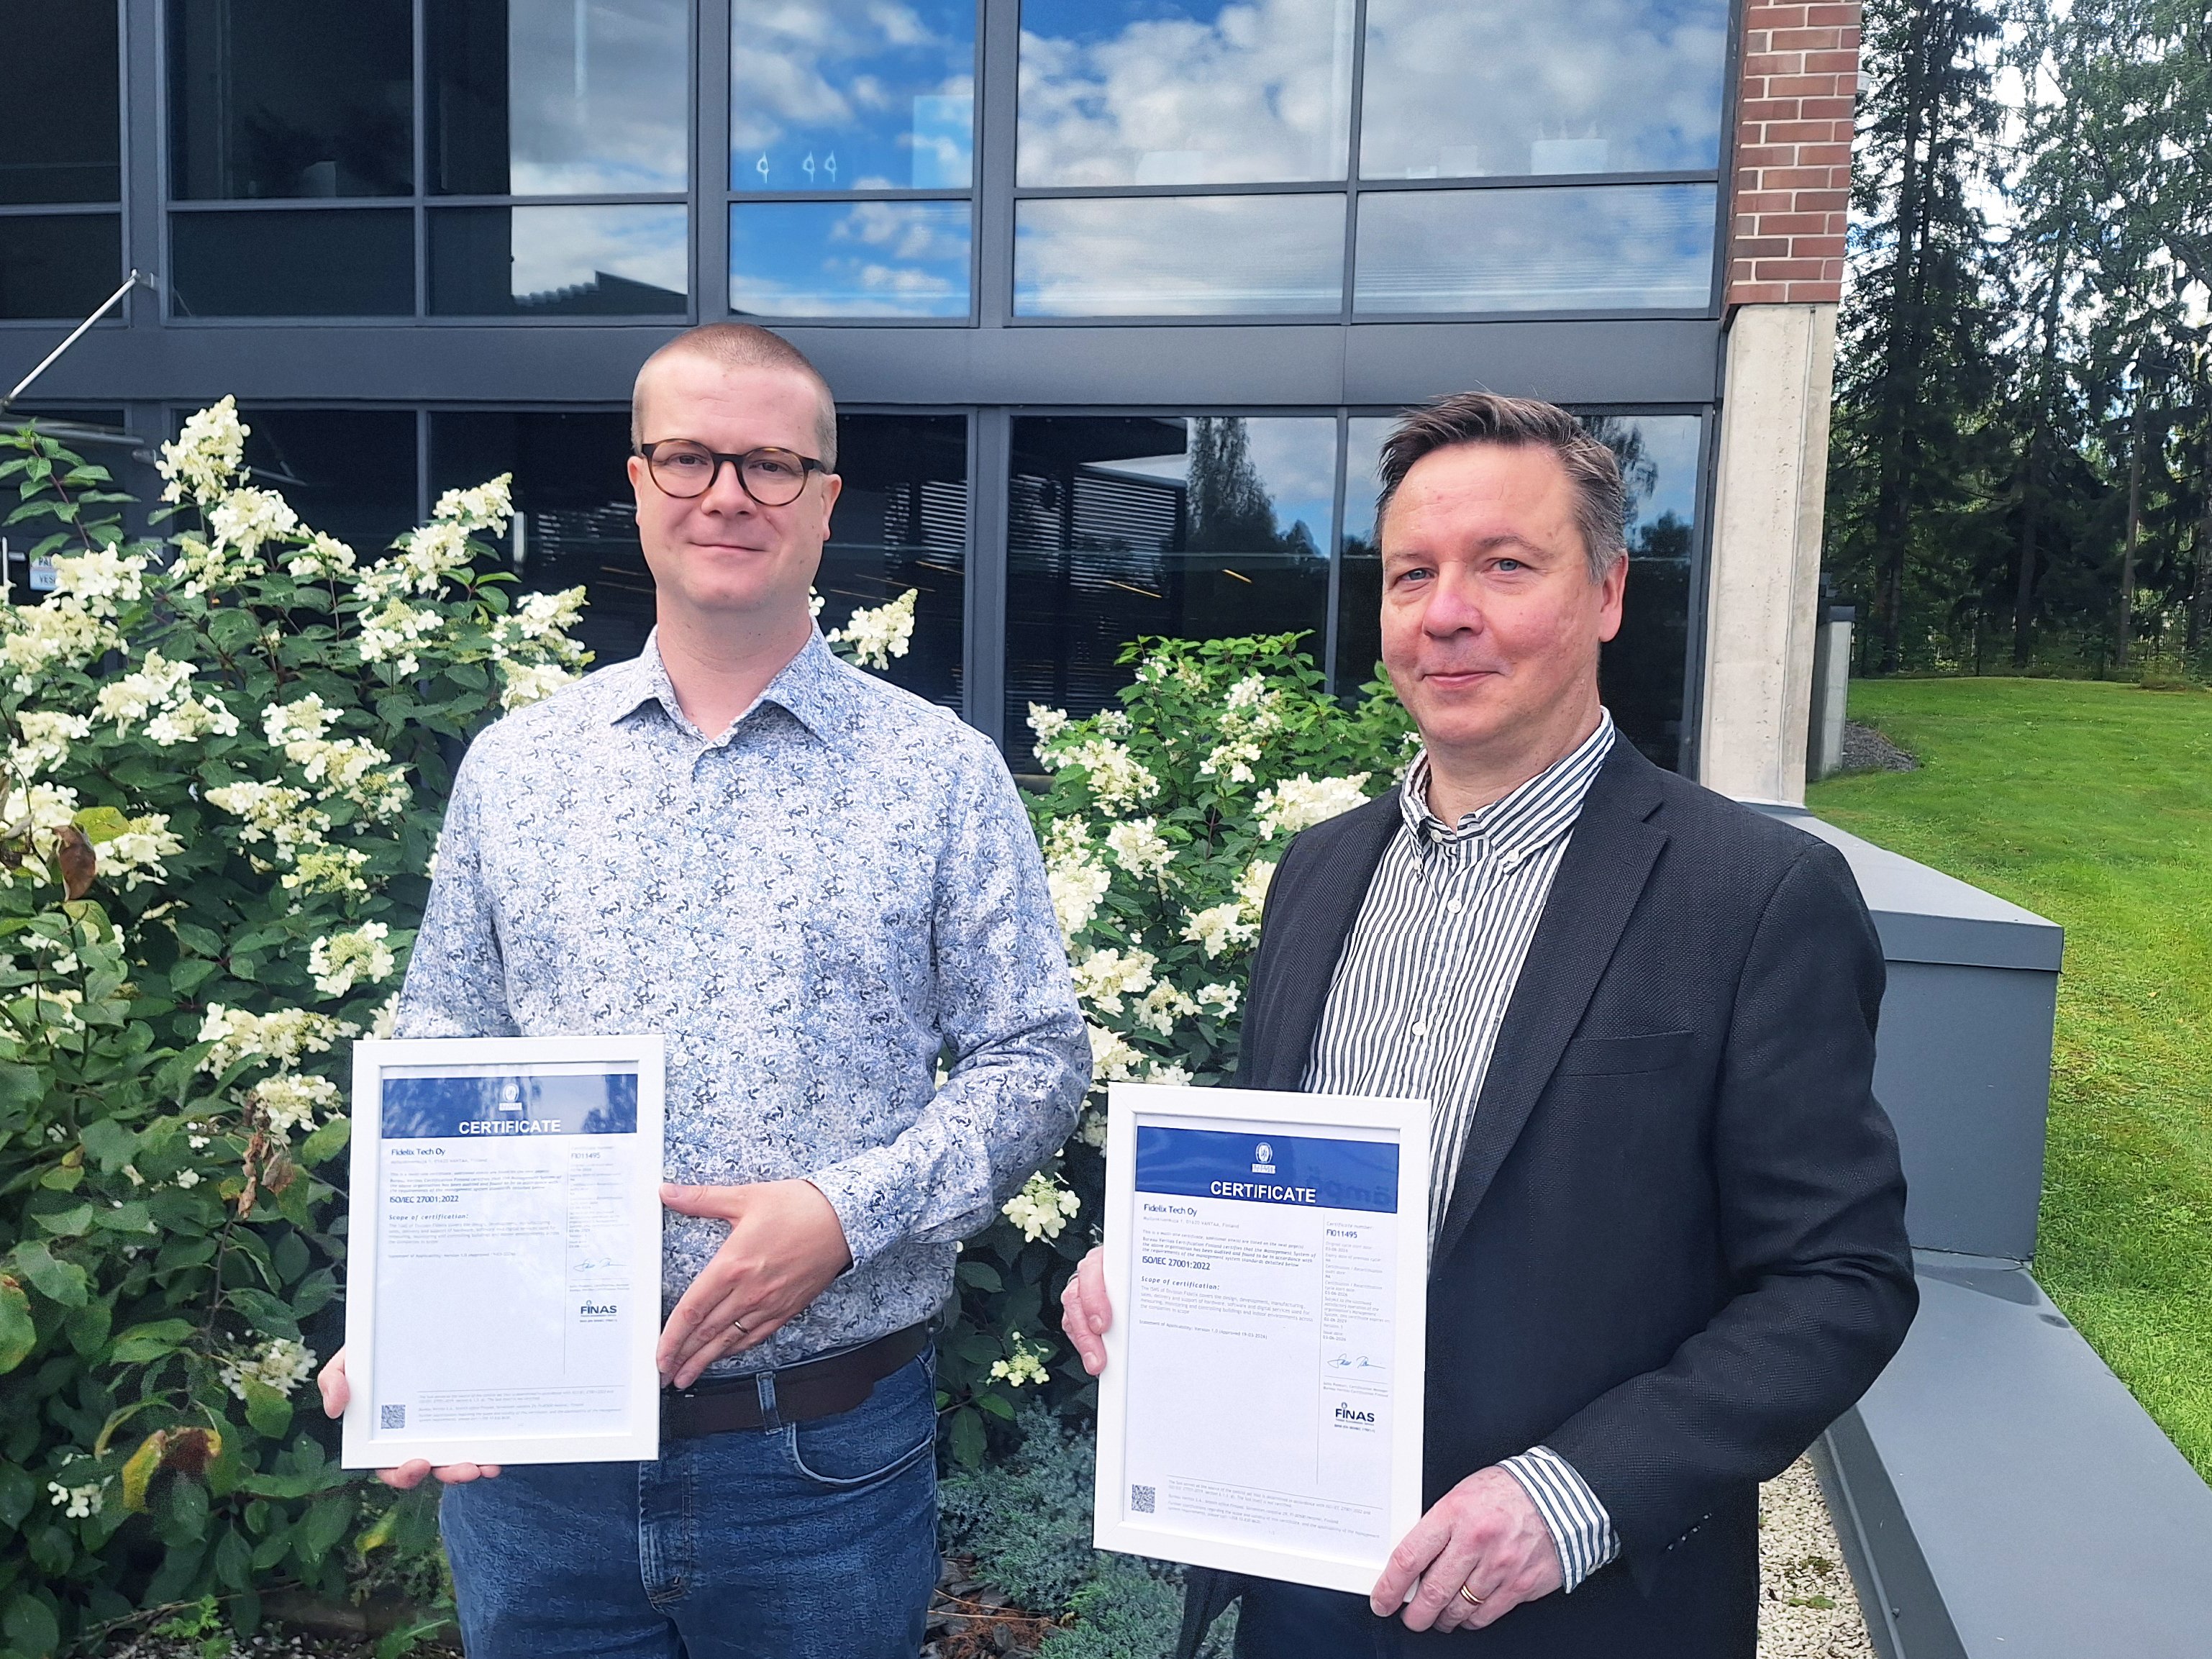 IT Manager Fredrik Bergstén and Senior Quality & Compliance Manager Timo Pellinen
ISO 27001 is the leading international standard for information security management. The certification provides independent verification that Fidelix companies manage and protect information in accordance with recognized global practices; covering their own operations as well as customer and partner data.
It also positions us ahead of tightening regulatory requirements, including NIS2, the Cyber Resilience Act and GDPR.
"Achieving ISO 27001 certification is a significant milestone for us. It reflects a long-term team effort to build a structured and effective information security management system across our companies," says Timo Pellinen, Senior Quality & Compliance Manager at Fidelix.
"At the same time, it confirms to our customers and partners that information security is embedded in our daily operations and not treated as a separate function."
Built on Shared Practices and Everyday Actions
Security is built into our products and services, supported by a culture grounded in risk thinking and shared responsibility.
In practice, this includes clear processes, continuous risk assessments and a strong focus on awareness, from employee training to consistent handling of information and reporting of potential risks.
“This achievement is the result of consistent work across the organization. It is built on everyday actions, from secure information handling and risk identification to following established processes. It strengthens trust with our customers and partners and supports our ability to operate in an increasingly regulated environment,” says Fredrik Bergstén, IT Manager at Fidelix.
Why Information Security Matters at Fidelix
Information security is particularly important at Fidelix because our systems operate at the interface of physical buildings and digital infrastructure. Our systems combine hardware, software and cloud services that our customers rely on every day. Protecting the integrity and availability of data is especially critical because these systems collect and process information to optimize building performance, indoor conditions and energy usage.
Our products and services cover the full lifecycle of customer systems, which means security must be maintained at every stage. It cannot be limited to product development or delivery alone; it has to extend into ongoing service and support functions as well. ISO 27001 provides us with a structured, internationally recognized framework for ensuring this. It embeds information security and risk management systematically into our processes, products and services across all Fidelix companies.
Looking Ahead: Integrated Security and Quality
Staying ahead in information security starts with knowing precisely what we're protecting. That's why Fidelix is integrating information security and quality management into a single, unified system, embedded consistently into everyday work, strengthening governance and helping us exceed customer and regulatory expectations.
More Information
Fidelix
Timo Pellinen
Senior Quality & Compliance Manager
timo.pellinen@fidelix.com
Fidelix
Fredrik Bergstén
IT Manager
fredrik.bergsten@fidelix.com


